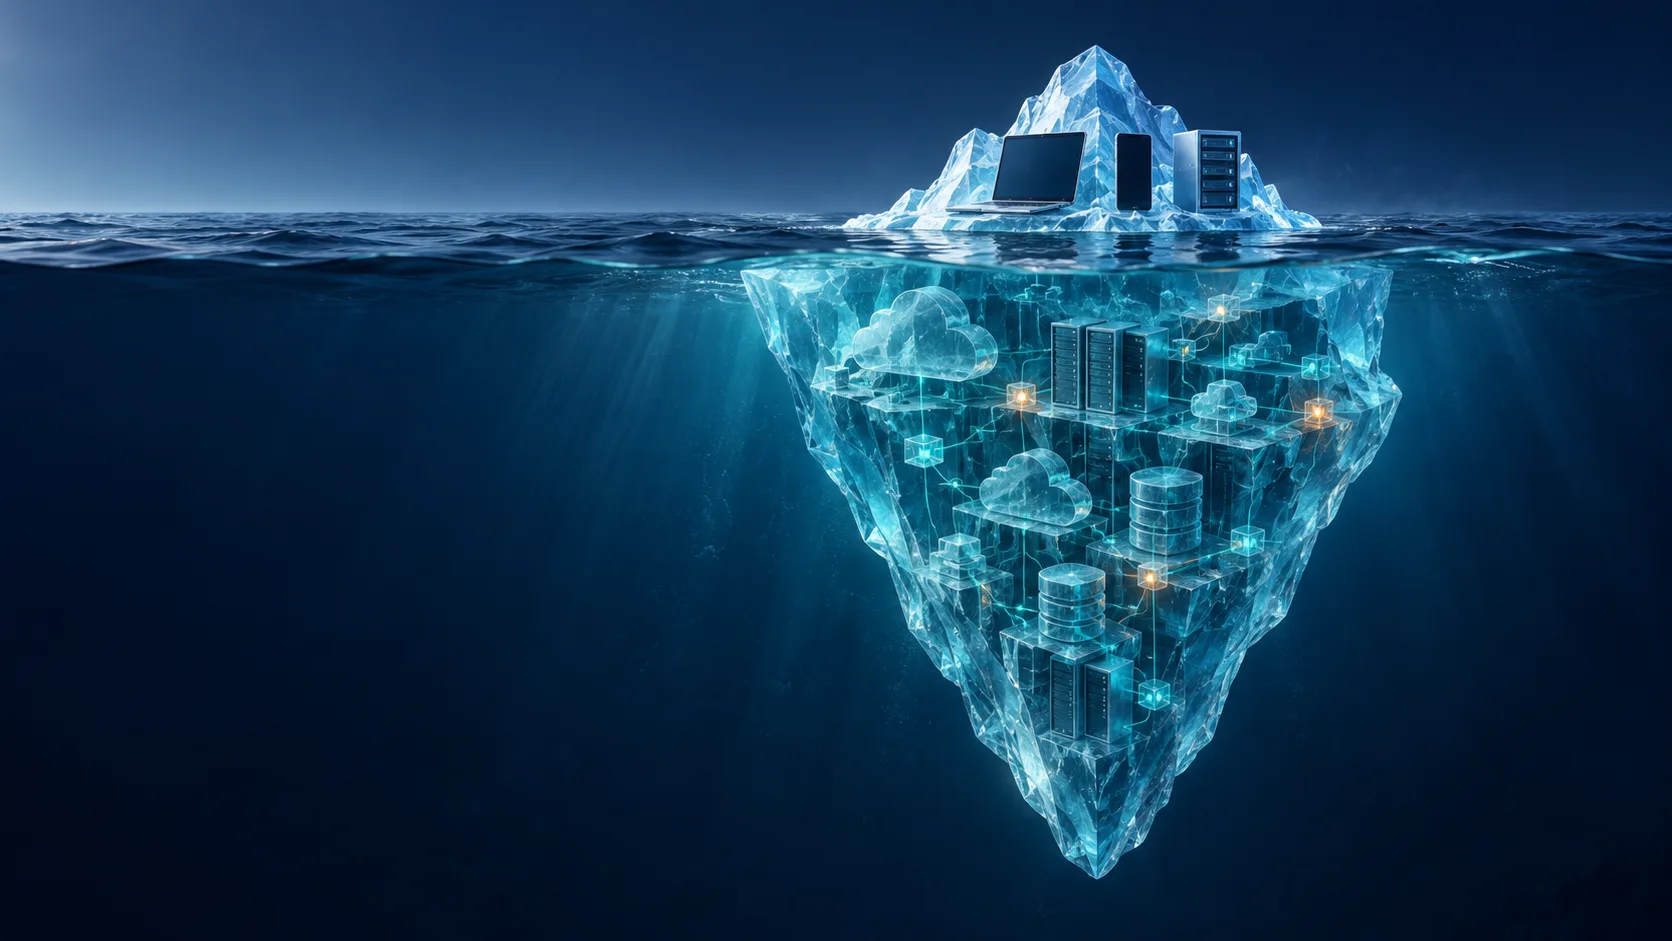
Somebody in your finance team has pasted a contract into a chatbot to summarise it. No board approved that, and no policy prevented it.
Key takeaways
- Assume AI adoption has already happened in your organisation informally, because it usually has, and without any policy behind it.
- Discover what is actually in use with telemetry you already own: identity sign-in logs, cloud app discovery and endpoint or browser reporting.
- Run the audit as a discovery exercise rather than a disciplinary one, since staff who expect consequences stop telling you anything useful.
- Choose between three proportionate responses for each tool found: sanction a safer version, contain its use, or replace it.
- Treat the audit findings as the first draft of your AI policy, because a policy written without them governs an organisation that does not exist.
At the first ramsac AI Summit in September 2026, one observation made the room noticeably uncomfortable. AI adoption has usually already happened inside an organisation, just not through a policy. That changes what leadership is actually deciding. The question is no longer whether to adopt AI. It is whether to find out what is already happening and put sensible boundaries around it before something goes wrong.
Adoption has already happened, just not through a policy
The pattern is recognisable once you look for it. Someone in finance summarises a contract in a chatbot because reading forty pages before a three o’clock meeting was not realistic. Someone in marketing drafts and publishes content without proof reading it . A team lead runs a spreadsheet through a free tool because the alternative was an afternoon of manual work.
None of these people is being reckless. Each is solving a genuine problem with a tool that is available, capable and free, and in most cases nobody has told them not to. That is worth holding onto, because it determines whether the audit finds anything.
The exposure is real nonetheless, and it is rarely where people expect. The headline fear is a model training on your data. The more common problems are duller: information leaving the organisation’s control entirely, work being done on personal accounts that remains after the the employee has left , and output being relied upon that nobody has checked.
Most organisations have dealt with shadow IT, and the instinct is to reach for the same playbook. The shapes are different in three ways that matter.
Shadow IT usually involves signing up for a service, which leaves a trail: an invoice, a domain, a login. Shadow AI often involves no signup at all, because the capability is built into software the organisation has already bought, or sits behind a free tier that requires nothing more than a browser.
Shadow IT tends to be a workaround for something the organisation does not provide. Shadow AI is frequently a workaround for something it does provide, but which is slower.
And the data exposure is immediate. Shadow IT typically stores data; shadow AI is usually given the data directly, in the body of a prompt, in a single action that is over before any control could intervene.
How to find out what is actually in use
The useful news is that most organisations already own the telemetry. A business running a mainstream cloud productivity platform has three sources available without buying anything.
- 🔍 Identity and sign-in logs. Where staff have signed into a third-party AI service using their work account, the identity platform has a record of it, including when it started and how many people are doing it.
- 💻 Cloud app discovery. Most security suites can report which cloud services are being reached from your network and managed devices, categorised by type, which surfaces tools nobody signed into with a work identity.
- 📃 Endpoint and browser reporting. Managed devices can report installed browser extensions and, where configured, flag large volumes of text being pasted into web applications.
Read together, these give a reasonable picture within a few days. What they will not catch is the person using a personal device on their own network, and it is worth being honest that no audit closes that gap. That one is addressed by making the sanctioned route good enough that the workaround stops being worth the effort.
What we typically see when this runs for the first time is a short list of tools nobody expected, a longer list of people using one or two mainstream assistants, and at least one genuinely useful workflow that somebody built quietly and never mentioned. That last category is worth as much as the risk findings.
Having the conversation without putting people on the defensive
How the audit is framed determines what it is worth. Announced as a compliance exercise with consequences attached, it produces a brief drop in detectable usage and a permanent drop in anyone telling you anything. The behaviour moves to personal devices, where you have no visibility at all and considerably less ability to help.
Framed as a discovery exercise, it produces something much more useful. The message that works is close to the truth: the organisation knows people are using these tools, it wants to understand which ones are genuinely helping so it can provide them properly, and it needs to know where information is going so it can keep that safe. Then say plainly that nobody is in trouble, and mean it.
It helps to ask directly alongside the technical work. A short, anonymous question to each team about what they use and what it saves them will surface things telemetry misses, and it signals that the exercise is about improvement rather than enforcement.
Three proportionate responses
Every tool the audit finds falls into one of three responses, and the temptation to apply the strictest one uniformly should be resisted.
Sanction it, with a safer version. This is the most common and most valuable outcome: people were reaching for a capability the organisation can provide properly, through a tool with the right data handling and an account that belongs to the business. The workflow survives, the exposure does not.
Contain it. Some tools are appropriate for certain work and not for other work. A tool without adequate audit logging might be fine for drafting internal material and unsuitable for anything touching client information. That is a boundary rather than a ban.
Replace it. A small number will be genuinely unsuitable, and for those the response is a prohibition that is enforced technically rather than by policy alone, paired with a supported alternative. A ban without an alternative simply relocates the behaviour.
Common questions
How do we find out which AI tools our staff are using?
Use the telemetry you already have: identity sign-in logs for third-party services accessed with work accounts, cloud app discovery from your security suite, and endpoint reporting for browser extensions. Combine it with a short anonymous question to each team, which surfaces what the logs miss.
Is shadow AI actually a risk for a smaller business?
Yes, though usually not in the way people fear. The common exposures are information leaving your control, work held in personal accounts that vanish when someone leaves, and unchecked output being relied upon. Those apply at any size.
Should we ban AI tools we have not approved?
Rarely as a first move. A ban without a sanctioned alternative moves the activity to personal devices where you have no visibility. Sanctioning a safer version of what people already reach for removes more risk than prohibition does.
From audit to policy
The reason to run the audit before writing the policy is simple. A policy drafted without it governs an imagined organisation, which is why so many read as generic and get quietly ignored. A policy drafted afterwards addresses the tools people actually use, the tasks they actually use them for, and the gaps that genuinely exist, which is why people follow it.
Run in that order, the audit stops being an exercise in finding out who broke the rules and becomes the thing that tells you what the rules should say. If you would like help running one, the discovery work sits within our managed cybersecurity services and uses tooling most organisations already have, and the policy that follows it is covered by our best practices for your AI governance framework. Where the audit raises broader questions about where to go next, our AI readiness assessment takes that view across the organisation.
Book an AI readiness assessment with ramsac to find out what your teams are already using, and get a proportionate plan for it.
AI Readiness Assessment
Book your AI Readiness Assessment with ramsac
We’ll help you uncover the most valuable opportunities for AI in your business and provide straightforward guidance on how to implement it safely, effectively and with confidence.